Jackie’s thoughts and research on cryptocurrency, privacy, and open source.
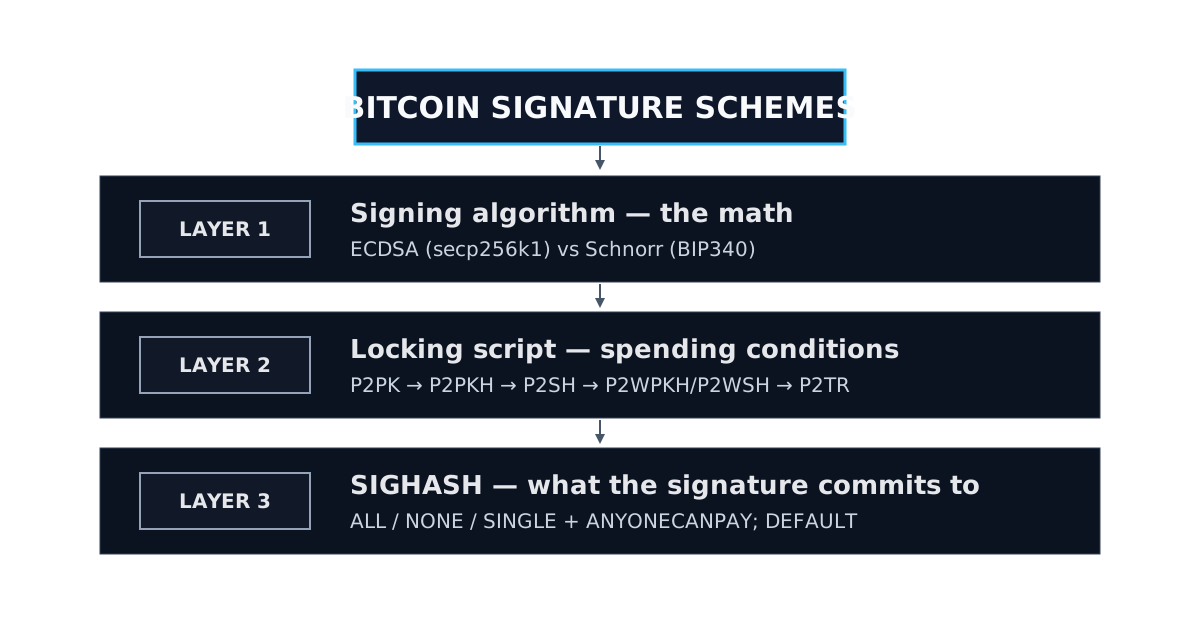
Bitcoin Signatures, Disentangled: ECDSA, Schnorr, Taproot, and SIGHASH
Bitcoin signatures split cleanly into three layers: the algorithm (ECDSA vs Schnorr), the locking script (P2PK, P2PKH, P2SH, SegWit, Taproot), and the SIGHASH commitment. Here is a layer-by-layer comparison of security, fees, and privacy, plus three approaches to multisig and a practical checklist.

How Proof of Reserves (PoR) Actually Works
A technical breakdown of Proof of Reserves: Merkle liability commitments, signed reserve addresses, what each party can verify, and the trust assumptions that remain.